Drift-Resilient and Adversarially Robust Federated Intrusion Detection for Industrial IoT
Drift-Resilient and Adversarially Robust Federated Intrusion Detection for Industrial IoT
Description
Details
Context and Problem Statement
Intrusion-detection models often perform well on static benchmarks but degrade in production as legitimate traffic evolves and new attacks appear. Industrial IoT also restricts centralized data collection, while attackers may manipulate both traffic inputs and federated updates.
Research Question
What trade-off exists among adversarial robustness, resilience to concept drift, and communication cost in a resource-constrained federated intrusion detector?
Proposed Approach
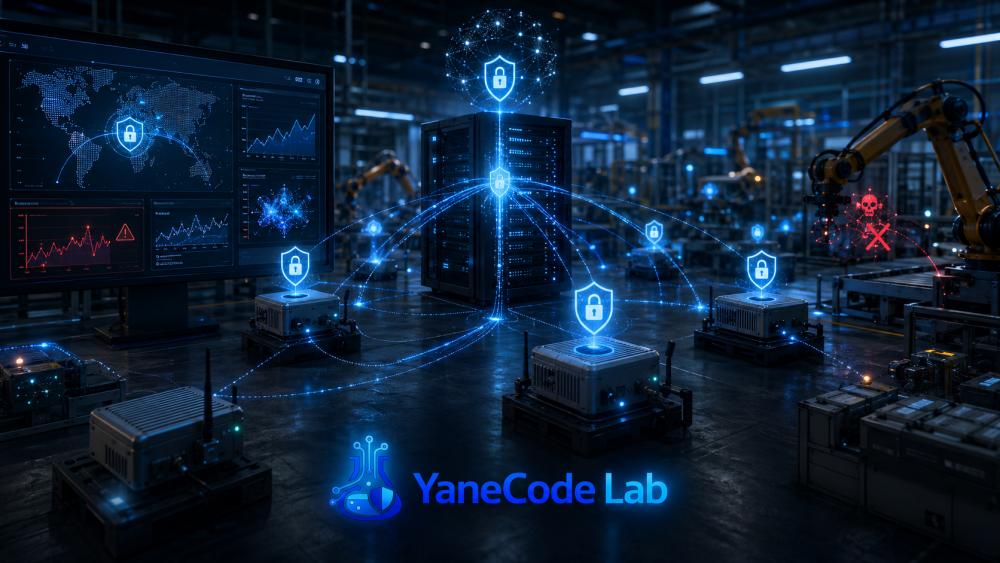
Build a federated platform with poisoning-resistant aggregation, statistical drift detection, bounded replay for continual learning, and protocol-valid adversarial perturbations.
Expected Contribution
An experimental characterization of the trade-off among drift resilience, poisoning resistance, adversarial robustness, and communication overhead.
Expected Prototype
A reproducible multi-gateway testbed with a dashboard displaying drift, performance degradation, and communication cost per round.
Datasets
Edge-IIoTset, TON_IoT, and CICIDS reorganized as temporally ordered streams.
Challenges
Protocol-valid adversarial evaluation, limited longitudinal data, extreme client heterogeneity, and defensive mechanisms becoming attack surfaces.
Research Question
Innovation
Expected Deliverable
Technologies
Required Skills
- Networks and Industrial Protocols
- Machine Learning and Federated Learning
- Defensive and Offensive Security in Controlled Environments
- Systems Programming and Containerization
Datasets
- Edge-IIoTset
- TON_IoT
- CICIDS2017 / CSE-CIC-IDS2018